Table of Contents
We built DNSAudit.io so people could run a serious DNS security scan without setting up anything. Open a browser, enter a domain, get results. That still works and it's still free for on-demand checks.
But a lot of the people using the platform are sysadmins, DevOps engineers, and security teams who live in the terminal. They've been asking for a way to run scans without switching context, wire checks into deployment pipelines, or just get JSON they can pipe into something else. That's what the CLI is for.
The DNSAudit CLI is a Go binary that talks directly to the DNSAudit.io API. No runtime dependencies, no configuration overhead. You authenticate once and every command just works.
Installation
The binary compiles to a single static file for each platform. You don't need Go installed on the target machine.
You can build from source:
git clone https://github.com/dnsauditio/dnsaudit-cli
cd dnsaudit-cli
go build -o dnsaudit main.go
Or grab a pre-built binary from the releases page for your platform. Supported targets:
- Linux - amd64 and arm64
- macOS - Intel and Apple Silicon
- Windows - amd64 and arm64
Move the binary to your PATH and you're done.
Authentication
Run dnsaudit configure once to save your DNSAudit.io API key to ~/.config/dnsaudit/config.json. For CI/CD pipelines and Docker environments, skip the config file and use the environment variable instead:
export DNSAUDIT_API_KEY="your-api-key"API access is currently in early access. Fill out the form and get your free API key today.
Commands
scan
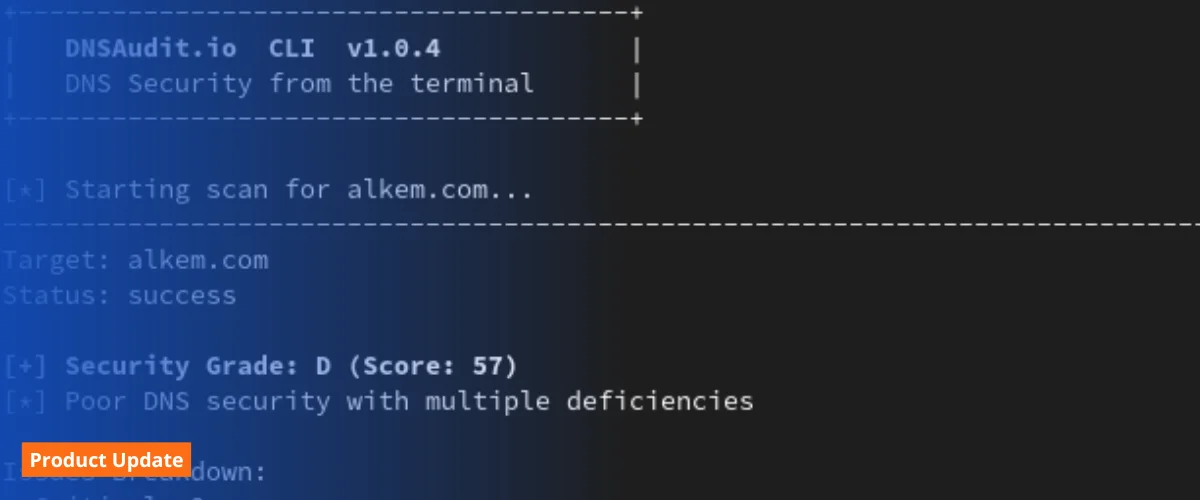
Runs a full DNS security audit against a domain and prints a formatted summary to your terminal. You get the security grade, issue counts by severity, and the top findings.
dnsaudit scan -d example.comStandard output:
[*] Starting scan for example.com...
---------------------------------------------------
Target: example.com
Status: success

[+] Security Grade: B+ (Score: 87)
[*] Good DNS security with minor improvements recommended

Issues Breakdown:
  Critical: 0
  Warning:  3
  Info:     8

Key Findings:
  [warning] DMARC: Missing DMARC Reporting Addresses
  [warning] CAA: Missing CAA records
  [warning] SPF: Missing Wildcard SPF for Subdomains
---------------------------------------------------
The scan covers the same checks available through the web interface, including DNSSEC validation, SPF, DMARC, DKIM, CAA records, nameserver redundancy, and more. To understand how individual checks are scored, the docs section walks through the details.
If you want raw JSON to pipe into jq or feed into a report template, add --json:
dnsaudit scan -d example.com -j | jq '.grade.score'
87
By default the CLI reuses a cached result when one is available for the domain. To force a fresh scan and bypass the cache, pass --no-cache:
dnsaudit scan -d example.com --no-cachehistory
Fetches your most recently scanned domains alongside their historical security scores. Useful for tracking a domain over time or cross-referencing a previous audit.
dnsaudit history --limit 20Pass --json for machine-readable output.
export
Downloads a full security report to disk in PDF or JSON format.
dnsaudit export -d example.com -f pdf
dnsaudit export -d example.com -f json -o output_file.json
The -o flag sets a custom output path. The default filename is <domain>-report.<format>.
Rate Limiting and Daily Limits
The CLI handles API rate limits gracefully. If the API returns a 429 due to burst limits, it parses the required wait time, pauses silently, and retries automatically. If you hit your daily scan limit, it exits with a clear error message. Daily limits are tied to your account plan.
Flags Reference
| Command | Flag | Description |
|---|---|---|
| Global | -h / --help | Show help for any command |
| scan | -d / --domain | Target domain (required) |
| -j / --json | Output raw JSON | |
| --no-cache | Bypass cached results and force a fresh scan | |
| history | -l / --limit | Max results to return (default 10, max 100) |
| -j / --json | Output raw JSON | |
| export | -d / --domain | Target domain (required) |
| -f / --format | pdf or json (default: pdf) | |
| -o / --output | Custom output file path |
What It's Good For
If you're doing security reviews across a portfolio of domains, the CLI makes it straightforward to script those audits and get consistent output every time.
If you're a DevOps engineer who wants a DNS sanity check as part of a deployment pipeline, wiring this in takes a few minutes.
If you're doing a pentest and need DNS findings in JSON, pass --json and pipe it where you need it.
The nameserver analyzer and the other interactive DNS tools on the platform are still the right choice for one-off checks in the browser. The CLI is for everything you'd want to automate or run against multiple domains on a schedule.
More background on how the platform approaches DNS security posture is on the about page.
Get Started
The first step is to request your API key access. That's the only requirement for the CLI to work.
This is an open source project under the MIT license. The full source is on GitHub. The integrations page has install instructions and platform notes, and the CLI documentation covers everything in detail.
If you run into anything, please get in touch. You can also open an issue directly on the repo.